Developers
Available via: Dashboard only
The Developers tab holds the credentials your integration uses to call Inflow, and the endpoints Inflow sends events to. It has three sections: API keys, SDK public keys and webhooks.
How to Access
- Open your Inflow Dashboard.
- Go to Settings → Developers.
What you see depends on your role:
- API keys and SDK public keys require access to API keys & SDK, which the Owner and Admin roles have by default. Creating and revoking keys requires write access.
- Webhooks require access to webhooks. Adding, editing and deleting them requires write access.
Two Keys, Two Purposes
| Key | Header | Where to use |
|---|---|---|
API key (inflow_prod_...) | X-Inflow-Api-Key | Server-side calls only: payments, subscriptions, refunds, customers, payouts and more. |
SDK public key (inflow_pub_prod_...) | X-Inflow-Public-Key | Client-side only, in the Inflow SDK payment form. |
Production keys work on live infrastructure. Sandbox keys use their own prefix and base URL; see Base URLs and Request Format.
API Keys
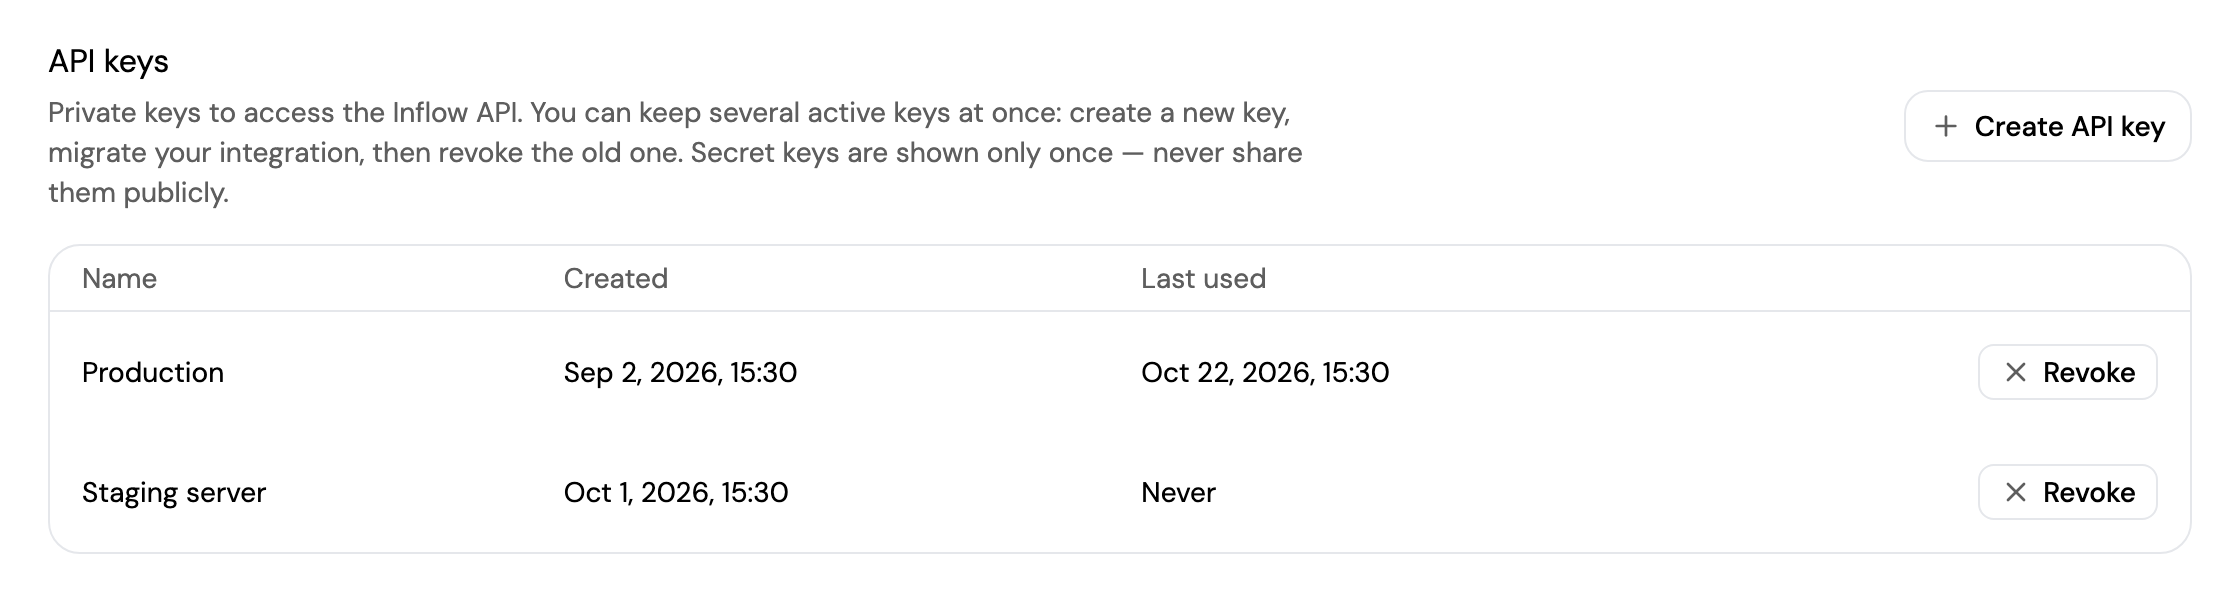
Your private keys to access the Inflow API. The table shows each key's Name, when it was Created and when it was Last used.
- Create a key: click Create API key and follow the steps. The key is shown only once, so copy it and store it securely straight away. If you lose it, create a new one.
- Revoke a key: click Revoke and confirm. The key stops working immediately, and any application still using it loses access.
You can have up to 5 active API keys at once.
Rotating a key
Your existing keys stay valid when you create a new one, so you can rotate without downtime:
- Create a new key.
- Update every environment that uses the old key, such as your server, CI secrets and deploy variables.
- Revoke the old key. Its Last used date helps you confirm nothing is still using it.
SDK Public Keys
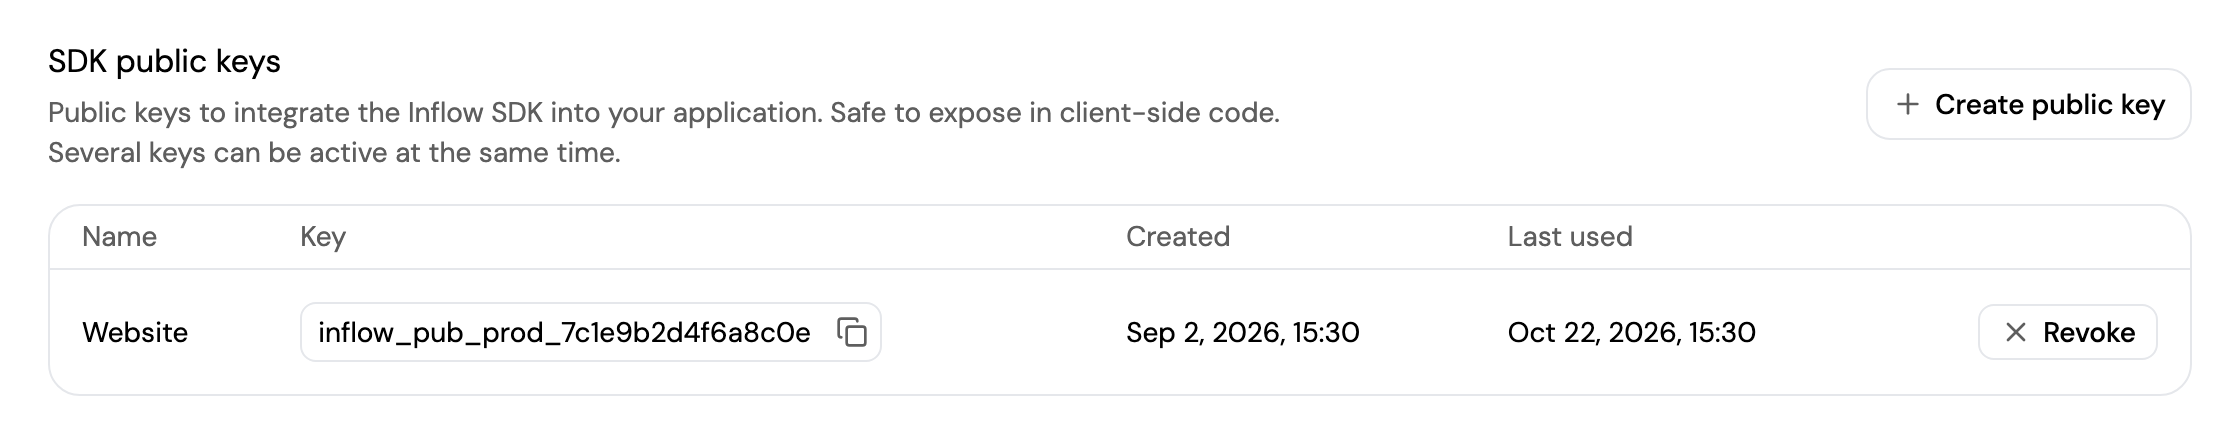
Public keys to integrate the Inflow SDK into your website or app. They're safe to expose in client-side code, and you can copy them from the table at any time.
- Create a key: click Create public key and follow the steps.
- Revoke a key: click Revoke and confirm. The key stops working immediately.
You can have up to 5 active SDK public keys at once.
Webhooks
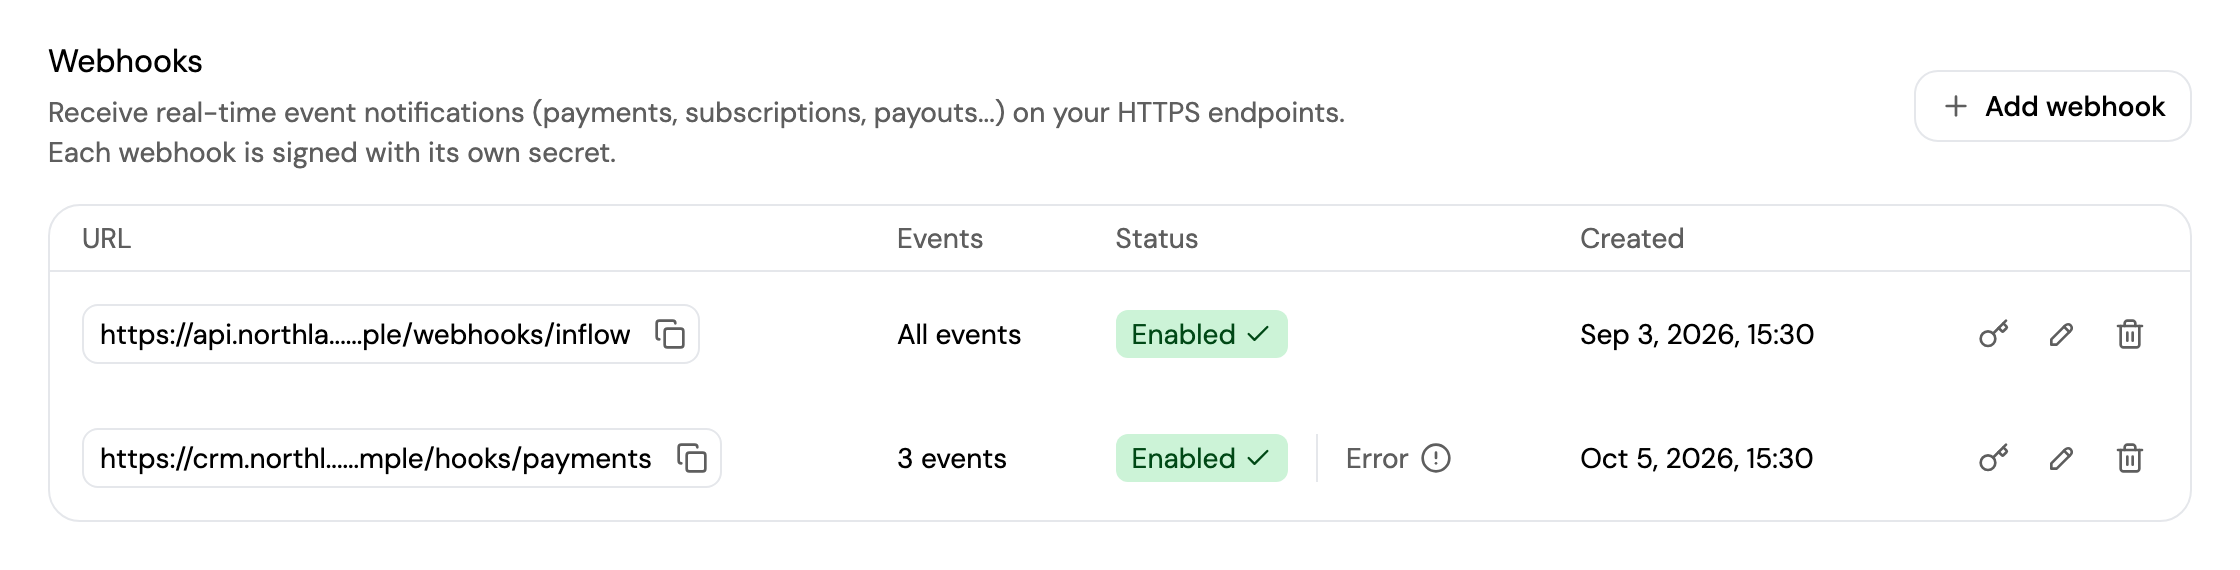
Inflow sends real-time events, such as payments, subscriptions and payouts, to your HTTPS endpoints. Each webhook is signed with its own secret.
| Column | Description |
|---|---|
| URL | Your endpoint. |
| Events | All events, or the number of events it's subscribed to. |
| Status | Enabled or Disabled. Error appears when the last delivery failed; click it to see why. |
| Created | When the webhook was added. |
- Add a webhook: click Add webhook and follow the steps: enter your HTTPS endpoint and choose the events to receive. Leave every event unchecked to receive all events.
- See its signing secret: click the key icon. Use the secret to verify the signature of the events you receive.
- Edit a webhook: click the pencil icon to change its URL or events, or to disable it.
- Delete a webhook: click the delete icon and confirm. Events are no longer sent to that endpoint.
You can have up to 5 webhooks. See Setting Up Webhooks for the events and their payloads.
Security Best Practices
- Never put your API key in frontend code. Keep it on your backend or in a secrets manager.
- The SDK public key is safe in the browser, but it only works with the SDK.
- Revoke a key straight away if it leaks, and when a teammate who had access to it leaves.
- Turn on two-factor authentication for every member who can manage your keys.
Related
- Get Your API Keys: quickstart for a first integration.
- Authentication & API Keys: request format and headers.
Updated 9 days ago