Team
Available via: Dashboard only
The Team tab is where you manage who has access to your Inflow account. Each teammate signs in with their own email and gets their access from a role: one of the four built-in roles, or a custom role you create.
How to Access
- Open your Inflow Dashboard.
- Go to Settings → Team.
Every member can see the team. Inviting, changing roles and removing members requires write access to team members, which the Owner and Admin roles have by default.
Team Members
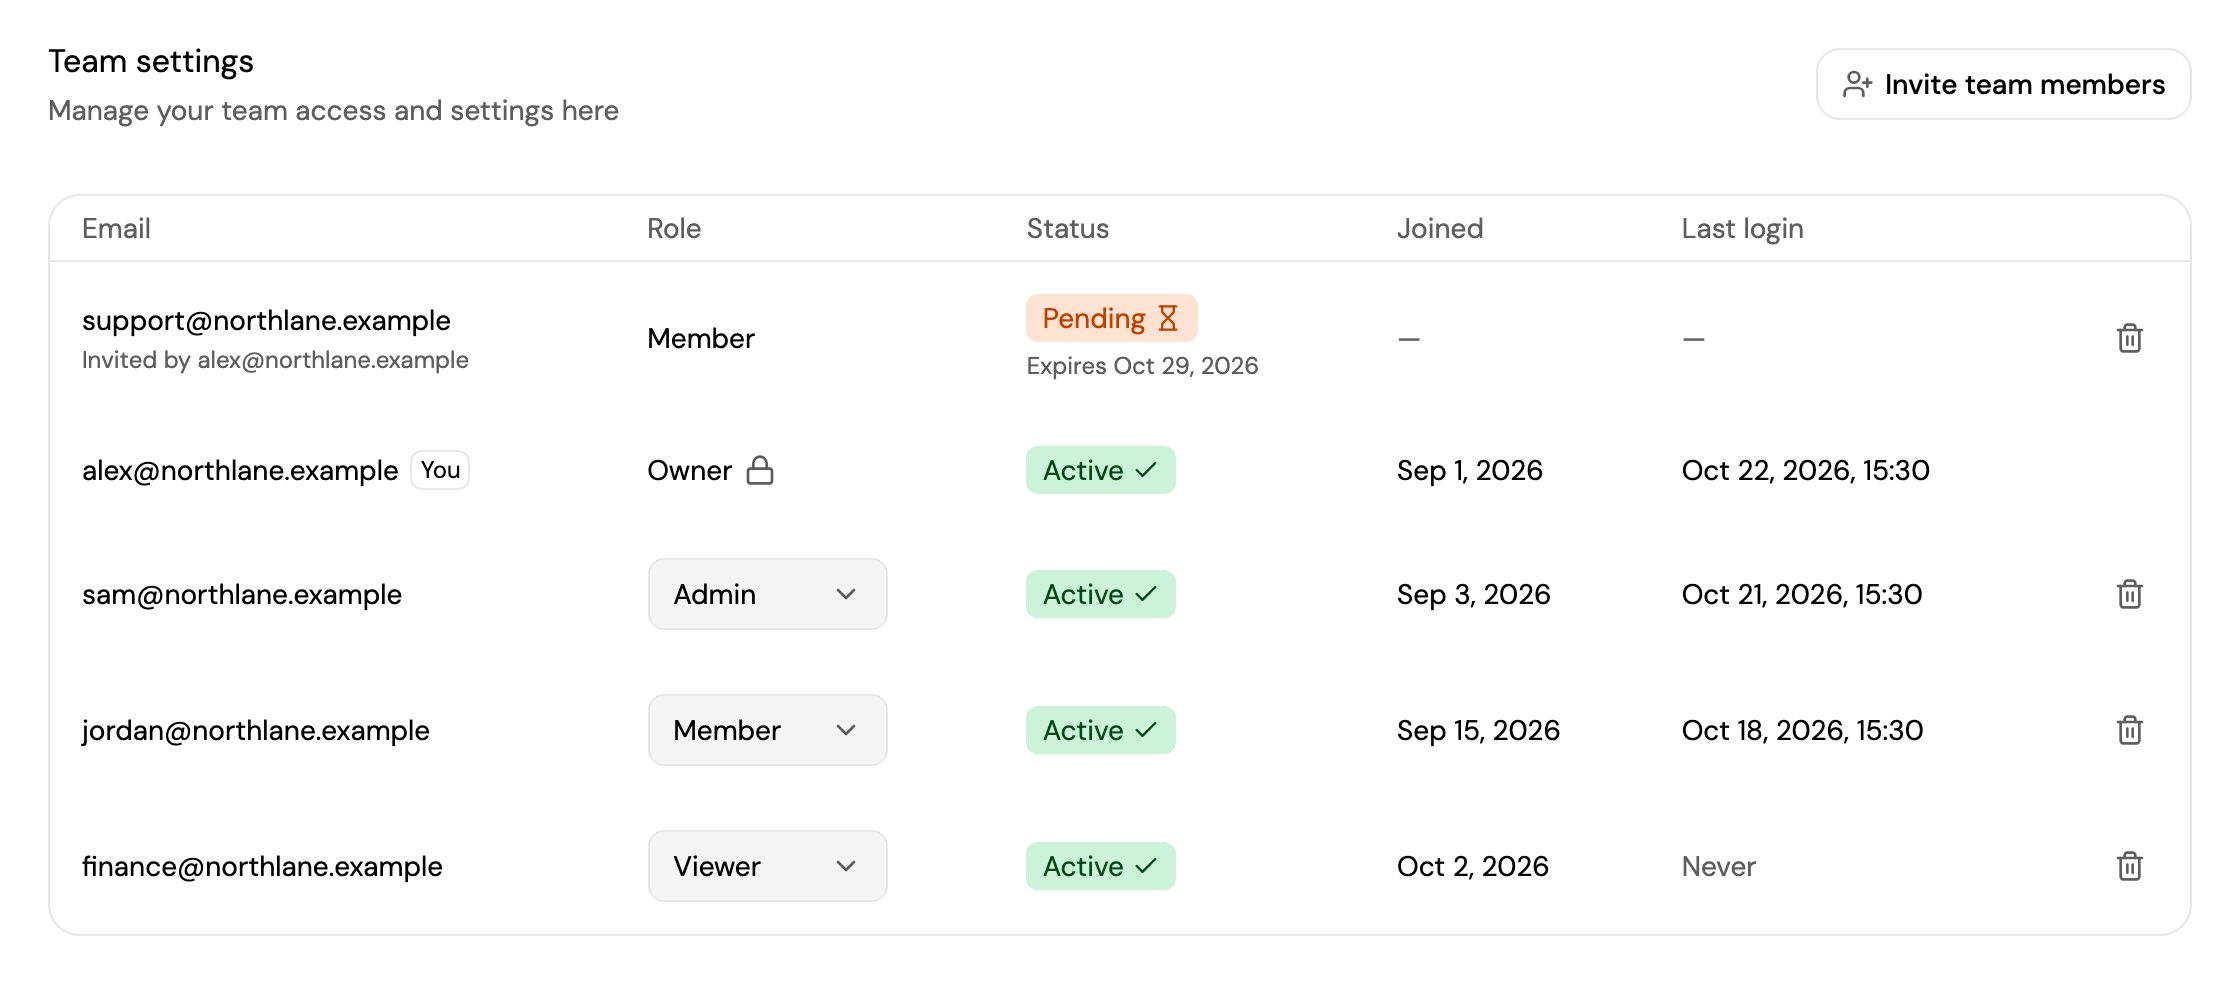
The table lists your teammates and the invitations that haven't been accepted yet.
| Column | Description |
|---|---|
| The teammate's email. You marks your own account; an invitation also shows who sent it. | |
| Role | The teammate's role. If you can change it, it's shown as a menu. |
| Status | Active, Inactive, or Pending for an invitation, with the date it expires. |
| Joined | When the teammate joined the account. |
| Last login | When the teammate last signed in, or Never. |
- Change a role: pick a new role from the menu. It applies immediately.
- Remove a member: click the delete icon and confirm. They lose access to the account right away; what they did before, such as approved payouts and issued refunds, stays in the account's history.
- Revoke an invitation: click the delete icon on a pending invitation and confirm. The invite link stops working.
A few rules apply:
- You can't change your own role or remove yourself.
- Only an Owner can change another Owner's role, and only an Owner or Admin can change an Admin's. Owners are shown with a lock.
- An account always keeps at least one Owner.
- An Admin can give the Admin, Member and Viewer roles and custom roles, but not Owner.
If you change the role of a teammate who is an approver in your Payout Approvals to a role below Admin, they're removed from the approvers.
Invite Team Members
Click Invite team members and follow the steps: enter one or more email addresses, separated by commas, choose a role and click Send invite. Each person receives an email with a link to join your account, and appears in the table as Pending until they accept.
Roles and Permissions
Every action in the dashboard needs a permission on a resource, at one of three levels:
- None: the resource is hidden.
- Read: view it.
- Read & write: view it and make changes. Write always includes read.
Built-in roles
| Role | Access |
|---|---|
| Owner | Full access to everything, including the payout approval policy, API keys and team roles. |
| Admin | Full access to payments, payouts, API keys and the team. Only the payout approval policy is reserved for Owners. |
| Member | Day-to-day operations: payments, links, subscriptions, customers and settings. Can view balances, payouts and the team, but can't send payouts, manage API keys or change team access. |
| Viewer | Read-only access. Can view payments, subscriptions, balances and settings, but can't change anything. |
The permissions behind each built-in role:
| Resource | Owner | Admin | Member | Viewer |
|---|---|---|---|---|
| Treasury & outgoing funds | ||||
| Balance & accounts | Read & write | Read & write | Read | Read |
| Payouts | Read & write | Read & write | Read | Read |
| Auto-payout | Read & write | Read & write | Read | Read |
| Payout policy | Read & write | None | None | None |
| Swaps | Read & write | Read & write | Read | None |
| Virtual accounts | Read & write | Read & write | Read & write | Read |
| Deposits | Read & write | Read & write | Read & write | Read |
| Payments & operations | ||||
| Payments, checkout sessions, payment links, subscriptions, subscription templates, products & prices, coupons, customers, disputes, activity | Read & write | Read & write | Read & write | Read |
| Developers | ||||
| API keys & SDK | Read & write | Read & write | None | None |
| Webhooks | Read & write | Read & write | Read & write | Read |
| Organization | ||||
| Team members | Read & write | Read & write | Read | Read |
| Merchant settings | Read & write | Read & write | Read & write | Read |
| Terms acceptance | Read & write | Read & write | Read | Read |
| Onboarding, Connect / marketplace, affiliates | Read & write | Read & write | Read & write | Read |
Only active Owners and Admins can be approvers in Payout Approvals. Some sensitive actions also ask for a code from your authenticator app, whatever your role; see Two-Factor Authentication.
Custom roles
When a built-in role doesn't fit, for example a support teammate who should manage subscriptions but never see payouts, create a custom role with exactly the access you need.
In Invite team members, under Roles, click Create role and follow the steps: name the role, optionally start from an existing role, and choose None, Read or Read & write for each resource. Click Manage roles to edit or delete your custom roles. Once created, a custom role can be assigned like any built-in role.
Custom roles follow these rules:
- Organization resources are always visible. Every role can at least read the Organization resources, so None isn't offered for them.
- You can only grant what you have. A role can't include a permission you don't have yourself. For example, an Admin can't create a role with access to the payout policy.
- Roles in use can't be deleted. Reassign the members and pending invitations that use a role before deleting it.
Common setups
| Goal | Role |
|---|---|
| Read-only teammate, such as an accountant or auditor | Viewer |
| Day-to-day operations without payouts or API keys | Member |
| Developer who manages API keys and webhooks | Admin, or a custom role with Read & write on API keys & SDK and webhooks |
| Support agent who handles subscriptions and customers only | A custom role with Read & write on subscriptions and customers, and None or Read elsewhere |
Best Practices
- Give Admin only to people who need to manage payouts, payout destinations, API keys or the team.
- When a teammate leaves, remove them and rotate any API keys they had access to.
- Turn on Payout Approvals so that no single person can withdraw your balance alone.
Updated 9 days ago